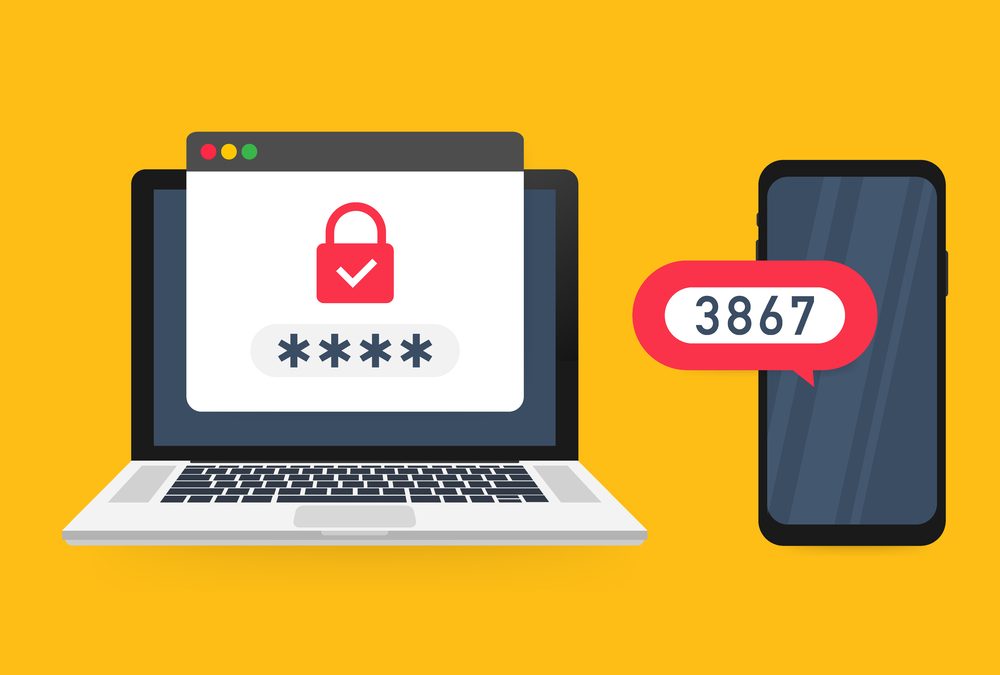
Multifactor authentication (MFA) to an information system, as described by The DoD, uses two or more methods of authentication involving something you know (e.g., password); something you have (e.g., a One-Time Password (OTP) generating device like a fob, smart-card, or a mobile app on a smart-phone); and something you are (e.g., a biometric like a fingerprint or iris). The traditional authentication method uses a single factor, typically a password, while multifactor authentication requires that a second factor also be used such as PIN sent via a text message (using something you have – the cell phone) or something you are (fingerprint). (Source)
Not all forms of MFA are equally secure. CISA and the DoW encourages organizations to implement phishing-resistant MFA. While any form of MFA is better than no MFA and will reduce an organization’s attack surface, phishing-resistant MFA is the gold standard and organizations should make migrating to it a high priority effort. (Source)